🎥 DevOps, IaC, and SRE
Nubenetes V2 Elite Portal
You are browsing the AI-Curated V2 Elite Edition. Looking for the exhaustive list of references? Check out the V1 Historical Archive.
Welcome to the DevOps, IaC, and SRE section of the V2 Video Hub. Explore curated high-density videos with architectural summaries.
Prometheus
🎬 Prometheus: The Documentary
Architectural Summary
This documentary explores the architectural genesis of Prometheus at SoundCloud, detailing how the shift to microservices necessitated a fundamental pivot from host-based monitoring to a pull-based, multi-dimensional metric data model. In a 2026 cloud-native context, understanding these foundational design decisions—specifically the trade-offs of localized TSDB storage, HTTP pull mechanics, and PromQL—is vital for architecting self-healing, high-cardinality observability pipelines across distributed, edge, and hybrid-cloud environments.

Terraform and Azure Verified Modules
🎬 Nubenetes Azure Verified Modules (AVM) Terraform Labs (Playlist)
Architectural Summary
Hands-on implementation labs and end-to-end Terraform walkthrough for Microsoft Azure Verified Modules (AVM). Covers toolchain setup (VS Code, Azure CLI, Terraform), Log Analytics centralized telemetry sinks, Azure Key Vault secret management, Storage Account Customer-Managed Key (CMK) encryption, Private Endpoints network isolation, zero public IP VM access via Azure Bastion, System-Assigned Managed Identity RBAC, and deterministic infrastructure lifecycle automation.
🎬 Nubenetes Azure Landing Zones 2026: Enterprise CAF and Architecture Blueprint (Playlist)
Architectural Summary
Comprehensive masterclass and enterprise reference architecture for Microsoft Cloud Adoption Framework (CAF) Azure Landing Zones (2026). Covers the retirement of the legacy monolithic CAF module in favor of Azure Verified Modules (AVM) and ALZ Library (2026.10.0), Management Groups hierarchy (Corp vs Online), Customer-Managed Hub-and-Spoke vs Microsoft-Managed Virtual WAN (vWAN), Private Endpoints vs Service Endpoints security perimeters, and Workload Identity Federation (OIDC) zero-secret CI/CD.
🎬 Azure Verified Modules Lab: Complete Terraform End-to-End Walkthrough
Architectural Summary
Hands-on technical walkthrough demonstrating how to compose and deploy production Azure infrastructure using Terraform Azure Verified Modules (AVM), enforcing RBAC, private endpoints, and diagnostic telemetry out of the box.
🎬 Retiring the CAF Monolith: Azure Verified Modules (AVM) and ALZ Library 2026
Architectural Summary
Explains the architectural migration from the legacy monolithic CAF Enterprise-Scale Terraform module to the decoupled Azure Landing Zones (ALZ) library and composable Azure Verified Modules (AVM).
🎬 ALZ 2026 Masterclass: Modular Architecture and AVM Rebuild
Architectural Summary
Comprehensive architectural masterclass analyzing the modular rebuild of Azure Landing Zones (ALZ) for 2026 using Terraform Azure Verified Modules (AVM) and policy-as-code guardrails.
🎬 How Azure Key Vault Secures Infrastructure | AVM Secret Management
Architectural Summary
Demonstrates how the Azure Verified Module for Key Vault (avm-res-keyvault-vault) provisions a hardened vault, generates cryptographic SSH keys in-cloud, and injects virtual machine credentials during Terraform deployments without exposing plaintext secrets on developer workstations.
🎬 How Local Code Builds Azure Clouds | AVM Terraform Labs Toolchain
Architectural Summary
Explains how platform engineers combine Visual Studio Code (with official Terraform schema validation), the Azure CLI (for authenticated Entra ID control-plane sessions), and the Terraform CLI to orchestrate deterministic Azure Verified Modules (AVM) deployments.
🎬 How Azure Verified Modules Automate CMK Encryption | Storage and Key Vault
Architectural Summary
Demonstrates how the Azure Verified Module for Storage Accounts (avm-res-storage-storageaccount) automates the Customer-Managed Key (CMK) cryptographic permission handshake in a single declarative Terraform block, provisioning Managed Identities and assigning Key Vault Crypto Officer roles automatically.
Terraform CI CD and GitOps
🎬 Day 0 to Day 2: Zero-Secret CI/CD Pipelines with GitHub Actions and OIDC
Architectural Summary
Architectural deep-dive into building zero-secret Terraform CI/CD pipelines from Day 0 bootstrap to Day 2 continuous operations using GitHub Actions and OpenID Connect (OIDC) Workload Identity Federation on Azure.
🎬 Azure Landing Zones 2026: Automated Framework and Zero-Secret CI/CD
Architectural Summary
Examines the automated bootstrap framework for Azure Landing Zones 2026, combining Terraform AVM starter modules with federated OIDC authentication and gated deployment environments.
Terraform Enterprise
🎬 Standardizing infrastructure automation with Terraform Enterprise
Architectural Summary
This presentation details AXA Group's cloud migration strategy (ATLAS) utilizing Terraform Enterprise as the cornerstone of their multi-cloud and private IaaS migration factory. It highlights how a highly regulated financial enterprise standardizes infrastructure-as-code (IaC) practices across multiple global subsidiaries to accelerate cloud adoption while maintaining governance. For a 2026 cloud-native landscape, this case study provides key insights into scaling self-service provisioning, implementing policy-as-code, and automating multi-tenant enterprise architectures at massive scale.

Terraform Testing and Validation
🎬 Azure Landing Zones Testing Strategies: Canary, Sandboxes and Non-Prod
Architectural Summary
Details multi-stage testing strategies for enterprise Infrastructure as Code, including sandbox management groups, canary policy rollouts, and automated Terraform validation gates.
FinOps and Cloud Cost Optimization
🎬 Nubenetes Azure Hybrid IaaS FinOps Framework (Playlist)
Architectural Summary
Enterprise FinOps architectural framework, mathematical break-even decision models, and continuous automation for hybrid Microsoft Azure IaaS environments (Windows Server, SQL Server on VMs, Hub-and-Spoke networking, ExpressRoute, and Azure Monitor). Covers Azure Hybrid Benefit (AHUB), Constrained vCPUs, Premium SSD v2 decoupling, edge log filtering via AMA and DCR, and sustainable cloud cost reduction ($173k to $39k/mo).
🎬 Nubenetes Kubernetes Rightsizing and FinOps (Playlist)
Architectural Summary
Pod failure analysis, container CPU/memory resource optimization, VPA/Goldilocks strategies, and AI-driven workload rightsizing for Kubernetes clusters.
HashiCorp Stack Terraform Vault Consul Boundary
🎬 Building a developer platform? Ask these questions.
Architectural Summary
This session details how to build secure, scalable developer platforms by defining 'golden paths' using HashiCorp's suite of automation tools, including Terraform, Vault, Consul, and Boundary. It provides a strategic framework for resolving key platform engineering challenges such as Day 2 operations, infrastructure dependency mapping, secure access control, and seamless local-to-remote environment transitions. By abstracting cloud complexity, the session demonstrates how to deliver high-velocity self-service capabilities to development teams while ensuring governance and security compliance.

eBPF and OpenTelemetry
🎬 Nubenetes Kubernetes and Multi-Cloud Observability with OpenTelemetry eBPF (OBI) (Playlist)
Architectural Summary
Architectural masterclass and production blueprints for multi-cloud Kubernetes observability using OpenTelemetry eBPF (OBI). Covers the multi-backend OpenTelemetry Collector routing blueprint, high-throughput tail-based sampling (80%-95% cost reduction), Grafana LGTM stack integration (tracesToLogsV2), and Zero-Grafana native observability across Red Hat OpenShift, Azure AKS, AWS, and GCP.
🎬 Nubenetes eBPF Metrics and Telemetry: Kernel Maps, OBI and Prometheus (Playlist)
Architectural Summary
Zero-code application RED metrics (Golden Signals), Linux kernel socket probes (sockops/tcp_recvmsg), self-monitoring eBPF map capacity, and Prometheus/Mimir Exemplars using OpenTelemetry eBPF (OBI). Covers multi-backend Collector pipelines, GitOps PrometheusRule alerting, multi-cloud architectures (OpenShift, AKS, EKS, GKE, SigNoz), and architectural boundaries.
🎬 Nubenetes Browser to Kernel: Full-Stack eBPF Observability (OBI) (Playlist)
Architectural Summary
Full-stack zero-code observability from client-side Single Page Applications (React, Angular) and Server-Side Rendering (Next.js, Node.js) down to Linux host kernel eBPF log enrichment using OpenTelemetry OBI. Covers W3C Trace Context (traceparent) propagation, frontend session correlation, and automated incident triage.
🎬 Nubenetes OpenTelemetry eBPF (OBI) Zero-Code Trace-Log Correlation (Playlist)
Architectural Summary
Production-ready architecture, Linux kernel internals, and incident triage workflows for zero-code trace-log correlation using OpenTelemetry eBPF Instrumentation (OBI). Covers in-flight trace ID injection, write/writev syscall tracing, async runtime caveats, and downstream pipeline tuning with Fluent Bit, Vector, and OpenTelemetry Collector.
ArgoCD and GitOps
🎬 Nubenetes ArgoCD and GitOps Automation (Playlist)
Architectural Summary
Declarative GitOps deployments, ArgoCD ApplicationSets, sync waves, multi-cluster architectures, and progressive delivery on Kubernetes and OpenShift.
Azure DevOps and GitHub Actions
🎬 Panel: Azure DevOps vs. GitHub Actions
Architectural Summary
This panel discussion provides a comprehensive architectural comparison between Azure DevOps and GitHub Actions, focusing on enterprise governance, extensibility, and CI/CD workflow migration strategies. It outlines decision frameworks for hybrid platform setups, highlighting how organizations can leverage GitHub Actions for modern cloud-native developer velocity while maintaining Azure DevOps for mature project management, test plans, and strict regulatory compliance. Essential for cloud architects planning long-term toolchain evolution, this session clarifies integration pathways and future-proof migration strategies.

DevSecOps
🎬 What is DevSecOps? DevSecOps explained in 8 Mins
Architectural Summary
This video details the transition from traditional, late-stage security audits to DevSecOps, explaining how shifting security left eliminates deployment bottlenecks in fast-paced delivery pipelines. It covers the automation of static analysis (SAST), software composition analysis (SCA), and container scanning directly within CI/CD workflows. In a 2026 cloud-native context, this paradigm is critical for securing ephemeral microservices and maintaining continuous compliance without sacrificing deployment velocity.

FinOps
🎬 The Brutal Truth Behind Tech Layoffs
Architectural Summary
This analysis dissects the macroeconomic shift from hyper-growth talent hoarding to hyper-efficiency, highlighting the systemic collapse of bloated engineering teams in favor of lean, automated operations. For a 2026 cloud-native landscape, this underscores the critical role of platform engineering and robust FinOps architectures designed to maximize resource utilization while minimizing human-in-the-loop operational overhead. Architects must leverage these insights to build self-healing, highly automated platforms that successfully decouple organizational scale from headcount.

GitOps
🎬 GitOps Guide to the Galaxy
Architectural Summary
Every other Thursday at 3pm ET hosts Hilliary Lipsig and Jonathan Rickard dive into everything in the GitOps universe, from solutions to common problems in end-to-end CICD pipelines, to creating Git workflows. This series explores how GitOps enhances modern application delivery and discusses the latest news around best practices and Cloud Native architecture.
Jenkins
🎬 Jenkins Tutorials
Architectural Summary
This comprehensive video series details core Jenkins CI/CD automation techniques, including Pipeline-as-Code implementations and system management best practices. In a 2026 cloud-native context, mastering Jenkins remains critical for orchestrating complex build pipelines, bridging the gap between legacy infrastructure and modern Kubernetes deployment targets. The tutorials provide foundational architectural patterns for establishing scalable, automated, and reproducible continuous integration workflows across distributed enterprise environments.
Terraform Azure Verified Modules AVM
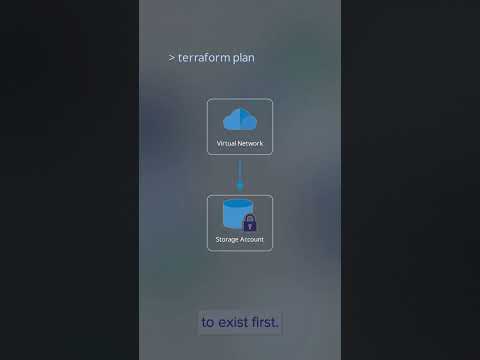
🎬 How Terraform Deploys Azure Verified Modules | AVM Lifecycle Short
Architectural Summary
This technical overview examines the four-phase Terraform provisioning lifecycle (init, plan, apply, destroy) utilizing Azure Verified Modules (AVM) to manage complex infrastructure dependencies like private VNet-integrated storage accounts. By mapping architectural relationships into a deterministic state file, it ensures predictable deployment ordering and complete teardown execution. In a 2026 Cloud Native context, adopting standardized modules with strict lifecycle management is essential for preventing configuration drift, eliminating orphaned cloud resources, and enforcing FinOps cost governance.
🎬 Deploying Secure Azure Architecture with Verified Modules | AVM Labs
Architectural Summary
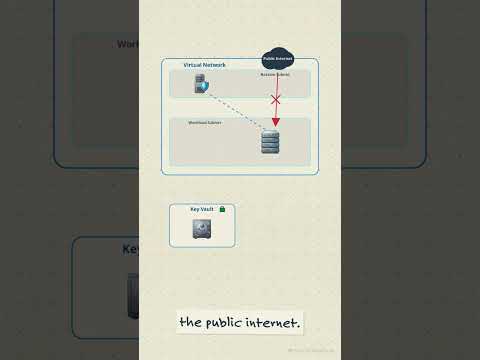
This video demonstrates how to rapidly provision a hardened, zero-trust Azure foundation using Microsoft's pre-vetted Terraform Azure Verified Modules (AVM) instead of maintaining thousands of lines of custom IaC. It showcases composable patterns that integrate Virtual Networks, automated SSH key vaulting in Azure Key Vault, zero-public-IP compute access via Azure Bastion, and passwordless Storage Account interactions through System-Assigned Managed Identities. In a 2026 Cloud Native context, adopting standardized, vendor-backed IaC modules accelerates deterministic infrastructure delivery while enforcing enterprise-grade security, private endpoints, and RBAC compliance by default.
Azure Private Link Terraform
🎬 How Azure Private Endpoints Lock Down Data | Private PaaS Security
Architectural Summary
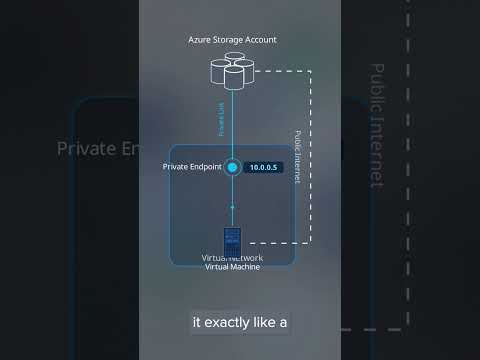
This video illustrates how Azure Private Endpoints secure cloud PaaS services like Azure Storage and Key Vault by projecting them directly into virtual network subnets using dedicated RFC 1918 private IP addresses. By integrating Private DNS Zones and eliminating public internet egress, this architecture ensures all sensitive data traffic remains locked within the internal cloud backbone. In a 2026 Cloud Native context, automating this zero-trust network isolation via Terraform and Azure Verified Modules (AVM) is critical for enforcing strict data perimeter compliance.
Azure Managed Identities Terraform
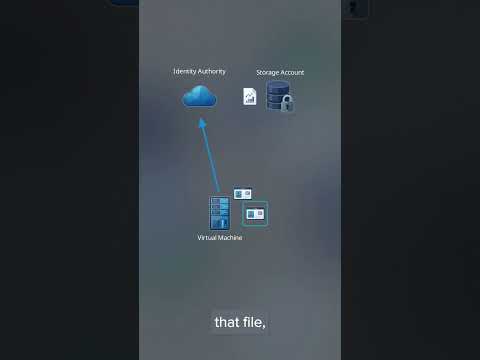
🎬 How Managed Identities Kill Passwords | Azure Zero-Secret Security
Architectural Summary
This video illustrates how Azure Managed Identities eliminate static credentials and connection strings in cloud-native architectures by binding workloads directly to Microsoft Entra ID. Rather than embedding vulnerable access keys in configuration files, resources dynamically obtain short-lived, automatically rotated tokens governed by granular RBAC permissions. Implementing this zero-secret pattern with Azure Verified Modules (AVM) in Terraform ensures automated credential lifecycle management and enforces strict least-privilege security postures across cloud environments.
Azure Bastion
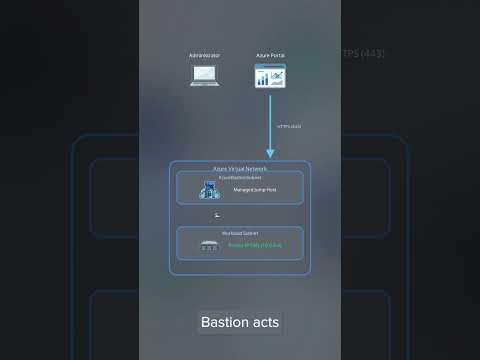
🎬 How Azure Bastion Secures Virtual Machines | Zero Public IP Access
Architectural Summary
This video explains how Azure Bastion enforces zero-trust network architecture by providing secure, seamless RDP and SSH connectivity to virtual machines directly through the Azure portal over TLS, completely eliminating the need for public IP addresses. In a 2026 Cloud Native and Infrastructure as Code (IaC) context—particularly when deployed via Terraform and Azure Verified Modules (AVM)—this pattern mitigates port scanning and brute-force attack vectors while standardizing hardened perimeter security across enterprise cloud environments.
Azure Managed Identities and Terraform
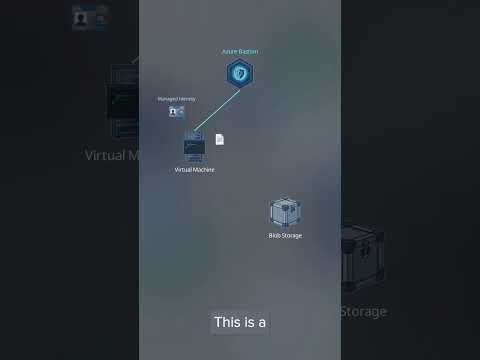
🎬 How Azure VMs Access Storage Without Passwords | Managed Identity RBAC
Architectural Summary
Shows how an Azure Virtual Machine provisioned with Azure Verified Modules authenticates via its System-Assigned Managed Identity (az login --identity) against the Azure Instance Metadata Service (IMDS) to access encrypted Blob Storage using RBAC without storing static keys or connection strings.
Terraform and Azure Verified Modules AVM
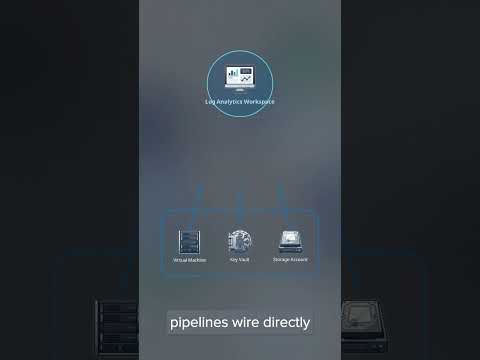
🎬 How Azure Centralizes Cloud Monitoring | AVM Log Analytics Workspace
Architectural Summary
This video demonstrates a 'telemetry-first' infrastructure deployment pattern using Azure Verified Modules (AVM) with Terraform to provision a centralized Log Analytics Workspace prior to compute or networking resources. By leveraging AVM's native shared diagnostic parameters, downstream components such as Virtual Machines, Key Vaults, and Storage Accounts automatically inherit telemetry bindings without repetitive custom diagnostic code. In a 2026 Cloud Native landscape, this standardized observability-as-code approach ensures zero-day visibility, instant cross-system correlation, and automated compliance auditing from the exact moment infrastructure goes live.
Terraform AzAPI and AzureRM
🎬 Why Azure Platform Teams Choose AzAPI Complexity | ALZ 2026 Architecture
Architectural Summary
This architectural overview explains why enterprise Azure platform teams strategically adopt the Terraform AzAPI provider alongside AzureRM to directly interface with the Azure Resource Manager (ARM) REST control plane. In a 2026 Cloud Native context, this dual-provider strategy eliminates upstream provider lag for day-zero security and compliance guardrails while leveraging plan-time OpenAPI schema validation. Central platform teams absorb the raw JSON complexity within Azure Verified Modules (AVM), empowering application teams with clean, composable abstractions for rapid deployment.
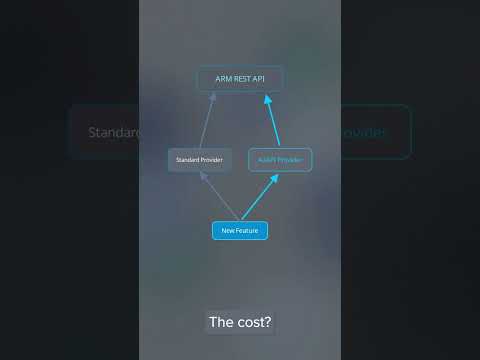
🎬 How AVM and AzAPI Beat AzureRM Updates | ALZ 2026 Architecture Takeaway
Architectural Summary
Explains how Azure Verified Modules (AVM) leverage the AzAPI provider under the hood to declare Azure Resource Manager (ARM) API properties directly, eliminating multi-month waiting periods for third-party provider updates while maintaining Microsoft-backed module interfaces.
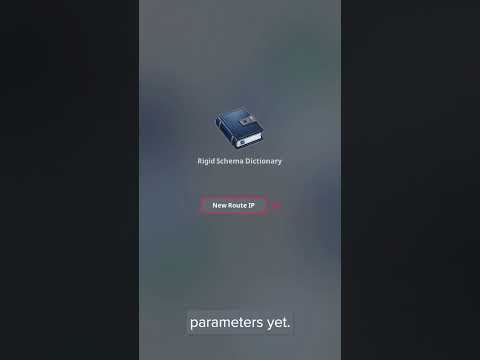
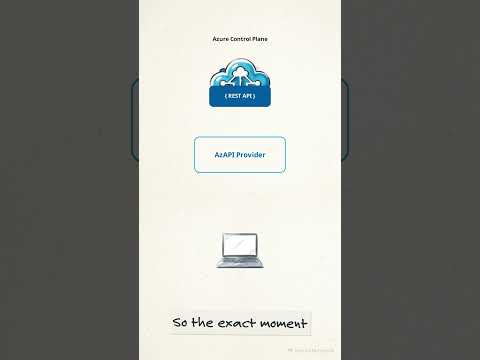
🎬 How AzAPI Enables Day Zero Deployments | ALZ 2026 Architecture Takeaway
Architectural Summary
Illustrates how the Terraform AzAPI provider enables Day-Zero deployments on Microsoft Azure by communicating directly with the Azure Resource Manager (ARM) REST control plane, allowing enterprise platform teams to adopt newly released Azure Landing Zone capabilities immediately.
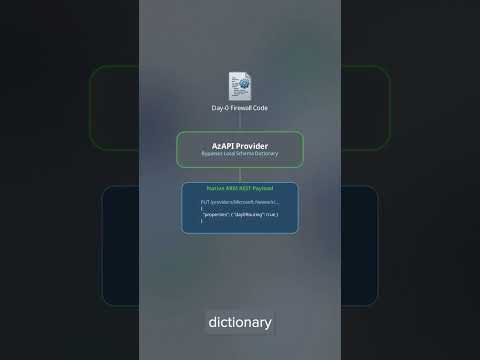
🎬 How AzAPI Unlocks Day Zero Azure Features | ALZ 2026 Architecture Takeaway
Architectural Summary
Details how platform engineers using Azure Verified Modules (AVM) and the AzAPI provider can pass raw ARM JSON payloads directly inside Terraform manifests to unlock preview and newly GA networking or security flags without provider bottlenecks.
Azure Storage Compliance and IaC
🎬 Nubenetes Azure Storage WORM and ERP Compliance (Spain Central) (Playlist) [SPANISH CONTENT]
Architectural Summary
Reference architecture and Infrastructure as Code (Terraform, Bicep, and Ansible) for immutable WORM storage on Azure Blob Storage (StorageV2) in the Spain Central (Madrid) region. Covers regulatory compliance with Article 30 of the Spanish Commercial Code (6-year legal retention), Anti-Fraud Law 11/2021, and VeriFactu Regulation (RD 1007/2023), achieving over 75% FinOps cost optimization via automated lifecycle tiering (Hot, Cool, Cold, Archive) and AEAT audit rehydration strategies. [SPANISH CONTENT]
SRE and Observability
🎬 Nubenetes SLAs and SLOs Observability (Playlist)
Architectural Summary
Comprehensive engineering guide to Service Level Agreements (SLAs), Service Level Objectives (SLOs), Service Level Indicators (SLIs), Error Budgets, and tail latency (P99) observability. Covers why averages lie in distributed microservices, Linux CFS CPU quota throttling, PromQL percentile math, canary deployment SLO gates, tail-based distributed tracing, and enterprise observability platforms.
🎬 Nubenetes Enterprise Observability and Monitoring Platforms (Playlist)
Architectural Summary
Comparative architecture, high-load stress testing, TCO modeling, and air-gapped monitoring strategies across 12 enterprise observability platforms.
🎬 Nubenetes Datadog on OpenShift (Playlist)
Architectural Summary
Deploying, tuning, and scaling the Datadog Agent and Operator on Red Hat OpenShift with Security Context Constraints (SCCs), edge log filtering, and FinOps ingestion cost control.
Zero-Trust IAM and OIDC
🎬 Nubenetes OAuth2, OIDC and Entra ID Identity on Azure (Playlist)
Architectural Summary
Architectural masterclasses, deep-dive podcasts, and technical walkthroughs on OAuth 2.0, OpenID Connect (OIDC), Microsoft Entra ID App Registrations, On-Behalf-Of (OBO) token exchange, Workload Identity Federation, and secretless zero-trust governance on Microsoft Azure with Terraform.
Jenkins and GitOps
🎬 Nubenetes Jenkins Pure GitOps (Without Git Parameter) (Playlist)
Architectural Summary
Declarative pull-based GitOps architectures, multi-cluster delivery with ArgoCD, and automated canary rollouts eliminating manual Jenkins UI Git Parameter dropdowns.
Jenkins CI CD Automation
🎬 Nubenetes Jenkins Git Parameter Automation (Playlist)
Architectural Summary
Enterprise immutable promotion, SCM tagging, release validation, and CI/CD pipelines using the Jenkins Git Parameter plugin and GitOps delivery patterns.
SRE and Decision Architecture
🎬 Nubenetes JevOps and System 1 Decision Models (Playlist)
Architectural Summary
Reflexive System 1 decision models for cloud-native infrastructure, submillisecond log filtering, and production deployment patterns on Kubernetes and OpenShift.
Keycloak and Enterprise IAM
🎬 Nubenetes Keycloak and RHBK Enterprise IAM on OpenShift (Playlist)
Architectural Summary
Enterprise identity architecture, Red Hat Build of Keycloak (RHBK), OAuth 2.1, OIDC federation, and multi-region high-availability replication on OpenShift.
Enterprise Modernization and GitOps
🎬 Nubenetes TIBCO BWCE Modernization and GitOps (Playlist)
Architectural Summary
Enterprise containerization, canary rollouts, Linux CFS CPU throttling tuning, and GitOps delivery pipelines for TIBCO BusinessWorks Container Edition (BWCE) on Kubernetes.
NetBox
🎬 NetBox Zero To Hero
Architectural Summary
NetBox serves as the foundational source of truth for modern network automation by integrating IP Address Management (IPAM) and Data Center Infrastructure Management (DCIM) into a unified database. In a 2026 Cloud Native ecosystem, it empowers Infrastructure as Code (IaC) pipelines to dynamically query and enforce intended network state via robust APIs, effectively eliminating configuration drift. This architectural approach bridges the gap between physical hardware tracking and automated, declarative network orchestration across complex hybrid environments.